Understand every signal.
Investigate what matters.
Beacon is a self-contained local cybersecurity workstation. Analyze offline PCAPs, stream real-time packet telemetry, explore heuristic subnet topology, and safely isolate threats—without external Python, Node.js, or cloud dependencies.
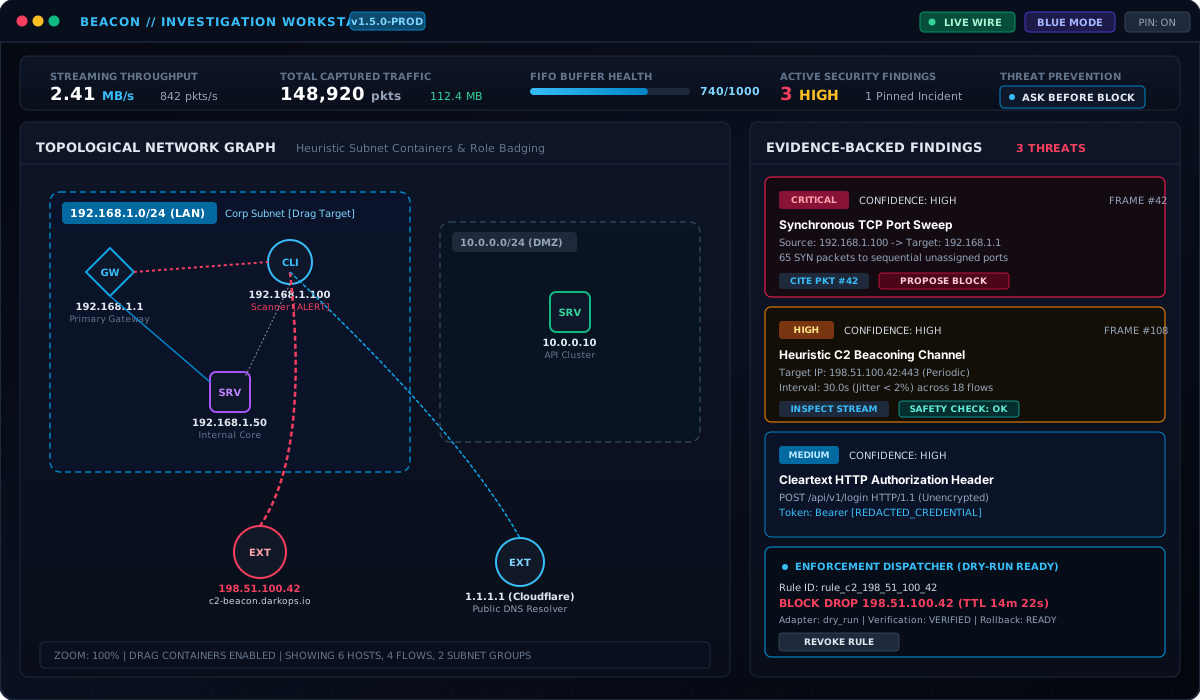
Built for Analysts Who Need Ground Truth
Beacon eliminates guesswork. Every alert cites exact packet numbers, every topology group reflects verified subnet arithmetic, and every threat mitigation is guarded by host-level verification.
See Your Network Without Manual Configuration
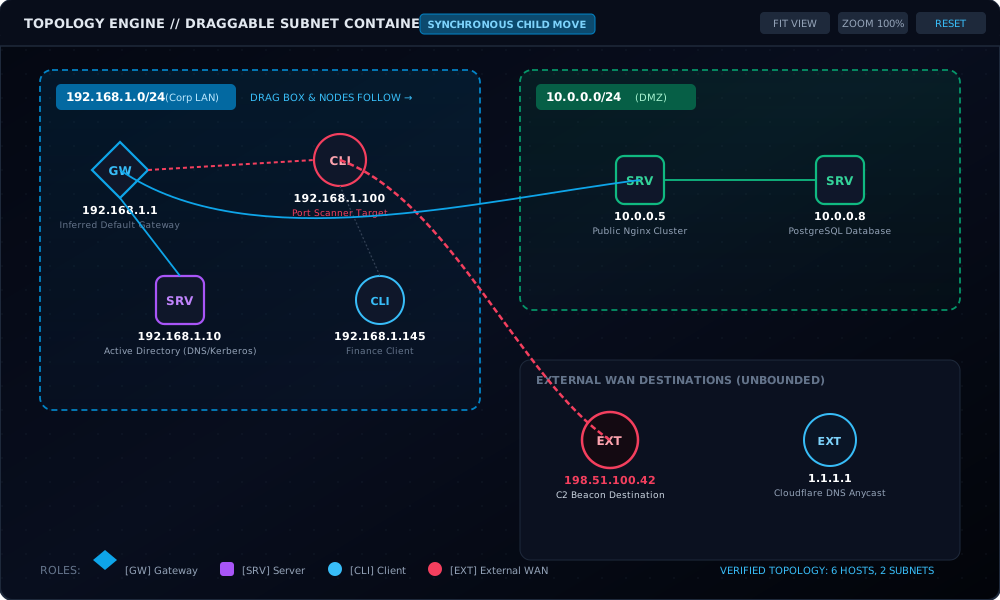
Beacon discovers your network structure heuristically. RFC 1918 subnets, default gateways, internal servers, and external endpoints are automatically categorized into visual containers.
- Synchronous Container Dragging: Moving a subnet box moves all child nodes and edge endpoints in lockstep.
-
Automatic Role Badging: Nodes are automatically tagged as
[GW]Gateway,[SRV]Server,[CLI]Client, or[EXT]External. - Cross-Subnet Flow Inspection: Click any connection edge to isolate conversations between subnets with full packet breakdown.
Zero "Vibe-Based" Detections
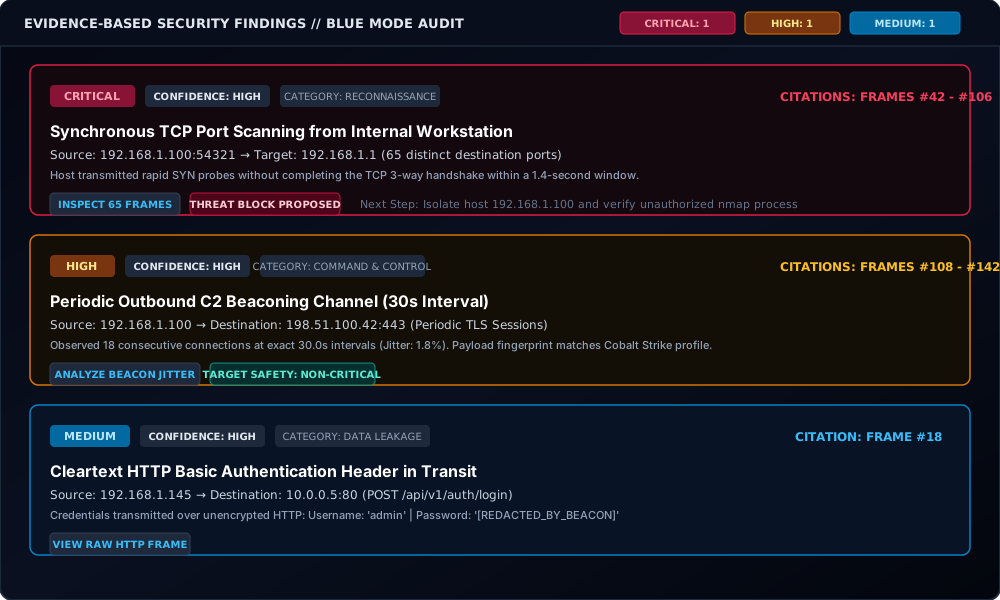
Security teams waste hours tracing hallucinations and vague AI alerts. Beacon grounds every single finding in verifiable packet frames, protocol indicators, and confidence ratings.
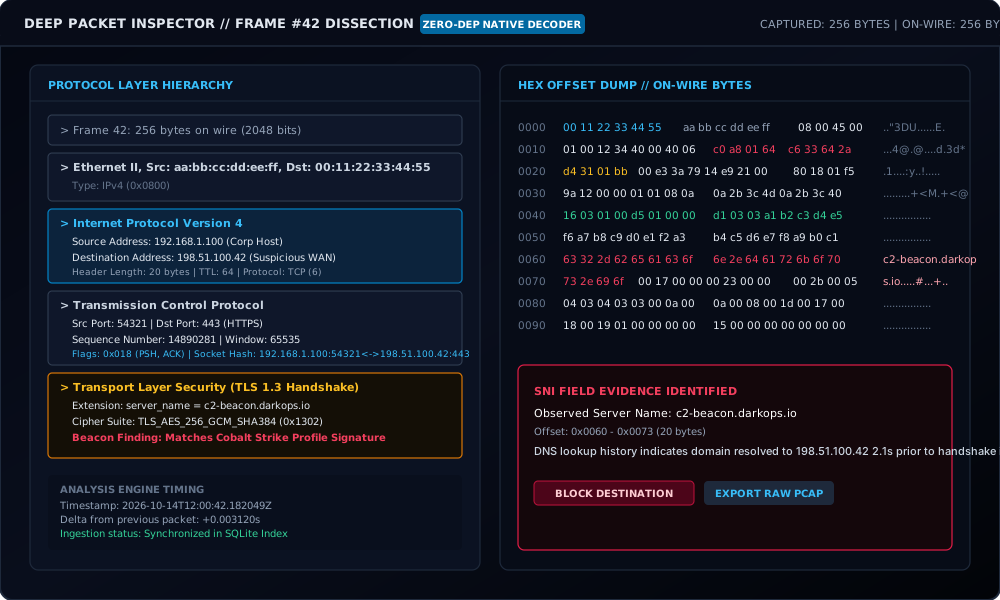
- Direct Frame Citations: Detections cite exact packet offsets (e.g., Frame #42, #108) with one-click jump to raw hex dumps.
- Dual Confidence Scoring: Independent severity and confidence indicators separate verified beacons from noisy heuristics.
- Audited Rule Engine: Port sweeps, SYN scans, Cobalt Strike beacons, ARP poisoning, and DNS tunnels detected out-of-the-box.
Full Packet Breakdown with Hex & ASCII Inspection
Drill down from layer 2 Ethernet framing to layer 7 application payloads. Inspect TLS Client Hello extensions, Server Name Indication (SNI), cipher suites, HTTP headers, and raw wire offsets.
- Dual Parsing Pipeline: Fast native pure-Python engine runs without dependencies, or leverages installed TShark for 1,000+ protocol decoders.
- Synchronized Hex Highlighting: Selecting a protocol tree node automatically highlights the exact byte range in the raw hex stream.
- Payload Extraction: Isolate suspicious payload signatures and IOC hashes directly from the analyst interface.
Continuous 24/7 Live Capture Center
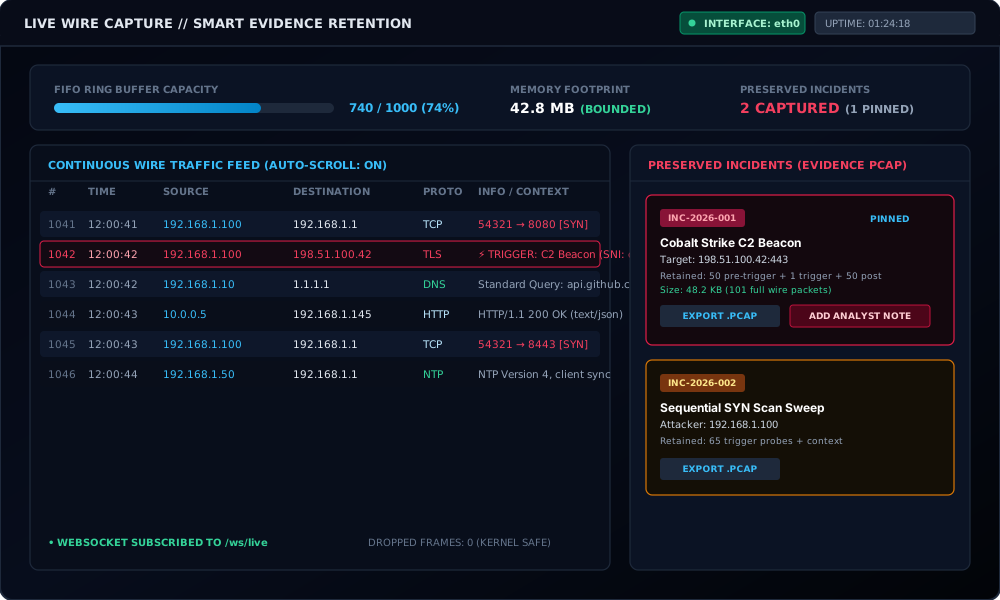
Capture live traffic directly from local network interfaces into a memory-bounded FIFO ring buffer. Retain critical incident packets indefinitely while normal background traffic cycles out.
- Bounded Memory Footprint: Strict configurable capacity limit prevents workstation memory starvation during gigabit bursts.
- Smart Incident Retention: Packets correlated with security findings are automatically pinned and preserved from FIFO eviction.
- Live WebSocket Telemetry: Streaming packet throughput metrics, protocol distributions, and instantaneous threat alerts.
Actionable Defense with Defensive Guardrails
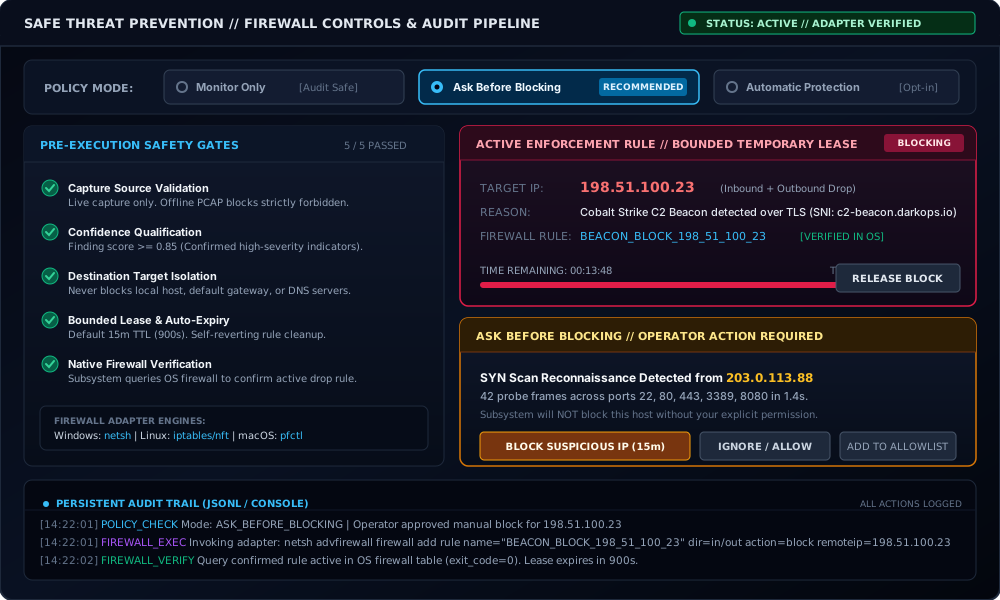
Unlike naive tools that blindly modify system firewall tables, Beacon enforces multi-stage safety gates, operator consent, temporary bounded leases, and post-execution verification.
- Three Strict Policy Modes: Defaults to Monitor Only. Enables Ask Before Blocking for manual sign-off, or Automatic for verified attacks.
- PCAP Immunity: Offline packet analyses are strictly forbidden from modifying firewall rules under any circumstances.
-
Native OS Adapters: Verified native firewall adapters for Windows (
netsh), Linux (iptables/nft), and macOS (pfctl).
Built with Precision, Tested with Rigor
Beacon is not a mock UI or a proof of concept. Every capability listed below is backed by existing source code, verified executables, and comprehensive automated test suites.
Pure-Python Offline PCAP Engine
Analyze standard PCAP and PCAPNG capture dumps immediately with zero external dependencies. The built-in pcap_native.py engine parses packet framing, protocol headers, and payload structures in pure Python.
TShark Accelerated Dissection
When Wireshark / TShark is detected in your PATH, Beacon seamlessly enables high-throughput deep dissection for more than 1,000 application-layer protocols, TLS handshake decrypts, and reassembled TCP streams.
Heuristic Subnet Clustering
Identifies subnets by inspecting broadcast, unicast, and ARP interaction patterns. Groups IP endpoints into logical CIDR clusters (e.g., 192.168.1.0/24) with automatic default gateway and DNS server discovery.
Synchronous Container Dragging
Reposition entire subnet boundaries across the interactive React Flow canvas without breaking topology layouts. Child node coordinates and communication edges reposition synchronously with zero visual lag.
Live FIFO Ring Buffer & Pinning
Live sniffing streams into a bounded FIFO memory ring buffer. High-severity security events automatically pin their correlated packet frames, safeguarding investigative evidence from circular memory eviction.
Safe Native Firewall Enforcement
Isolate malicious endpoints safely using native OS firewall tools (Windows Netsh, Linux iptables/nftables, macOS pfctl). Features 5 pre-execution safety gates, automatic 15-minute lease expiry, and audit verification.
PIN Auth & Brute-Force Rate Limiting
Protect analyst dashboards on local networks with cryptographic PIN verification, secure HTTP headers, and strict endpoint rate limiting to prevent unauthorized LAN surveillance access.
Self-Contained Native Binaries
Packaged with PyInstaller into single-file native executables. Double-click Beacon.exe on Windows or execute Beacon on Linux to start immediately without configuring virtual environments.
High-Fidelity React Workstation
Engineered with modern React 18, Tailwind CSS, Lucide icons, and React Flow. Features dark obsidian aesthetics, responsive navigation, and real-time WebSocket telemetry charts.
Rigorous Automated Test Coverage
Every release is verified against a 157-test automated verification suite covering parser corner cases, live capture buffers, topology heuristics, API security, and firewall rollbacks.
Threat Prevention Engineered for Safety
Automated firewall blocking is notorious for bricking networks when misconfigured. Beacon was built from the ground up with fail-safe boundaries, operator approval gates, and time-bounded leases.
Configurable Enforcement Policies
Monitor Only Default
Alerts and findings are logged with evidence citations, but zero system firewall rules are ever created. Ideal for audits and compliance monitoring.
Ask Before Blocking Recommended
When high-confidence threats appear, Beacon alerts the analyst and prompts for approval before invoking the OS firewall adapter.
Automatic Protection Opt-in
Autonomous defense for live capture feeds. Automatically blocks verified malicious external destination IPs subject to strict rate limits and confidence thresholds.
5 Pre-Execution Safety Validation Gates
127.0.0.1), RFC broadcast ranges, local subnets, or detected default gateway routers.
Modular & Resilient Architecture
Beacon separates ingestion, dissection, heuristic correlation, defensive enforcement, and presentation into decoupled layers.
Ingestion Layer
Supports drag-and-drop PCAP/PCAPNG files and live network interface capture with memory-bounded ring buffers.
Dissection Engine
Dual-engine parser: lightweight zero-dependency native Python reader with optional TShark acceleration for 1000+ protocols.
Correlation & Rules
Evidence-based detection pipeline mapping suspicious behaviors, port sweeps, C2 beacons, and subnet topology relationships.
Workstation UI
React 18 frontend with interactive React Flow topology canvases, real-time WebSocket telemetry, and hex byte-level inspector.
Engineering Honesty: The Physical Switch Limitation
Many network tools dishonestly claim: "Run this on your laptop and see every packet across your entire company network!"
In computer networking, that is physically impossible on a standard Ethernet switch.
Standard Layer 2 network switches learn MAC addresses and deliver unicast traffic only to the specific destination port. A workstation running Beacon on an ordinary switch port will only see its own traffic plus local broadcast/multicast (ARP, DHCP, mDNS)—not unicast traffic between two other machines.
To inspect multi-device traffic across your LAN, use one of these three standard industry approaches:
1. Managed Switch Port Mirroring (SPAN)
Configure your managed switch (Cisco, Ubiquiti, TP-Link, Netgear) to mirror all port traffic to the analyst monitoring port running Beacon.
2. Passive Hardware Network TAP
Place an inline hardware TAP (Throwing Star, Dualcomm, Profitap) between your router and core switch, feeding mirrored packets directly to Beacon.
3. Gateway / Firewall Deployment
Run Beacon directly on the default gateway or router (e.g., Linux router, pfSense box, or planned sensor daemon) where all egress flows pass through.
Download Beacon for Your Platform
Fully self-contained executables. Double-click to start Beacon, launch your default browser, and begin analyzing. Zero runtime installation required.
Tested and verified on clean Windows 10/11 64-bit systems. Automatically bundles the complete Python runtime, dependencies, and built React UI into a single self-extracting executable.
.\Beacon.exe
Standalone ELF executable compiled for Linux x86_64. Contains all core libraries, offline parser, web dashboard, and firewall adapters (iptables/nftables).
chmod +x Beacon && ./Beacon
macOS build specification is available in the repository. Currently undergoing validation matrix before official signed binary publication.
python -m beacon.cli serve
Up and Running in 60 Seconds
No complex setup scripts, database installations, or cloud credentials. Start investigating packets immediately.
Download Binary
Grab the single-file executable for Windows or Linux from the downloads section or GitHub Releases.
Launch Application
Double-click the executable. Beacon boots the embedded web server and opens your default browser.
Load Traffic
Drag and drop any PCAP/PCAPNG capture file into the window, or click "Start Live Capture" to sniff your interface.
Investigate Evidence
Explore subnet clustering, click cited packet numbers, review suspicious C2 signals, and review safe firewall rules.
Product Roadmap
What is currently delivered and verified, versus what is planned for upcoming milestones.
Architecture Foundation & Offline PCAP Engine
Initial release establishing zero-dependency pure-Python packet parsing, baseline CLI, and proof-of-concept network topology visualization.
Self-Contained Workstation & Safe Threat Prevention
Zero-dependency pure-Python offline PCAP parser, TShark acceleration, heuristic subnet grouping, synchronous container dragging in React Flow, 24/7 FIFO live ring buffer, safe host firewall adapters (Windows netsh, Linux iptables, macOS pfctl), 15-minute auto-expiring rules, PIN rate limiting, and single-file Windows (37.8 MB) and Linux (28.8 MB) binaries. 157 passing tests.
Headless Sensor Daemon & Advanced Dissectors
Lightweight headless background sensor daemon for Raspberry Pi and Linux-based routers (OpenWrt). Automatic TLS Client Hello fingerprinting (JA3/JA4), SSH banner anomaly checks, and extended DNS tunneling entropy heuristics.
Multi-Sensor Mesh & Threat Intelligence Feeds
Centralized analyst console aggregating packet alerts from multiple distributed Beacon sensor nodes across remote subnets. Optional offline threat intelligence feed correlation (MISP, abuse.ch, AlienVault OTX) with local cryptographic caching.